The presence of a record that the Nikke PC launcher was executed does not necessarily indicate that hacking damage occurred. According to a technical report by GitHub user MotherSphere, in one infection case, a remote control agent was installed only 3 times during approximately 19 launches of the launcher. In the other 16 instances, nothing appeared to happen. The issue is that during the brief periods when the agent was actually installed, users have almost no way to directly verify which files the attacker read from their PC. This incident demonstrates that files from the CDN (Content Delivery Network), the official content distribution channel operated by the game company, were tampered with, potentially allowing users' PCs to be remotely controlled.
How Tampered Official Files Invoke Malicious Code
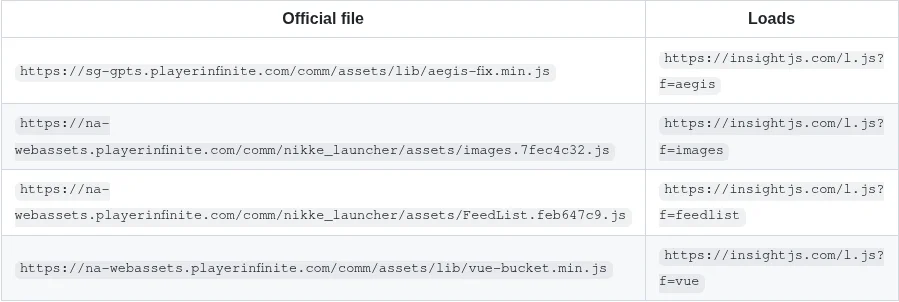
A CDN is a globally distributed storage system set up by game companies to rapidly deliver heavy assets, such as graphics and audio files, to users. Every time the Nikke PC launcher runs, it accepts and executes JavaScript (JS) code files from Level Infinite's CDN, the service operator. MotherSphere's analysis confirmed that code added by the attacker had been mixed into four official files (aegis-fix.min.js, vue-bucket.min.js, images.7fec4c32.js, FeedList.feb647c9.js) in this repository from September 27, 2026 onward 1.
These files, which users believed they were executing as normal code, used hidden commands to download and install a remote control agent program separately from an external server (insightjs.com). Once the agent was installed, the PC came under the attacker's remote control while the Nikke PC launcher remained open. MotherSphere explained that this agent connected to the attacker's server approximately every 30 minutes to await commands. When the attacker sent an 'execute' signal, the attacker could perform the same actions as the user 12.
It has not yet been confirmed how the attacker obtained permission to modify these official files 12. However, as of the early morning of November 4 (KST), Level Infinite conducted an update to replace the tampered files with normal code 13. Nevertheless, already infected PCs are not automatically cleaned, so individual checks are necessary.
Information Targeted by the Remote Agent and How to Check for Infection
On a PC where the agent was installed, a total of 264 specific paths were automatically traversed. This included passwords stored in six browsers, such as Chrome, Edge, and Firefox, and 28 types of cryptocurrency wallet files 12. Additionally, developer security files, such as SSH keys, cloud access credentials, and authentication files for AI coding tools, were included in this list 12. However, detailed command records of which files the attacker read and when are not left in the launcher logs or Windows execution history 2. As a result, it is difficult for users to prove directly whether data was actually leaked from their PC.
The most specific way to check if the agent entered and executed on your PC is to search the log file in the installation folder. Open the Launcher/intl_service/debug.log file inside the folder where Nikke is installed with a text editor and search for the string 'k2f_chan' 12. In the log of the infected PC analyzed by MotherSphere, traces of agent execution were recorded consecutively in the following pattern.
"lua downloaded to log\tinyget\tinyget.<timestamp>.log"
"k2f_chan registered"
"agent started as <PC 이름>"
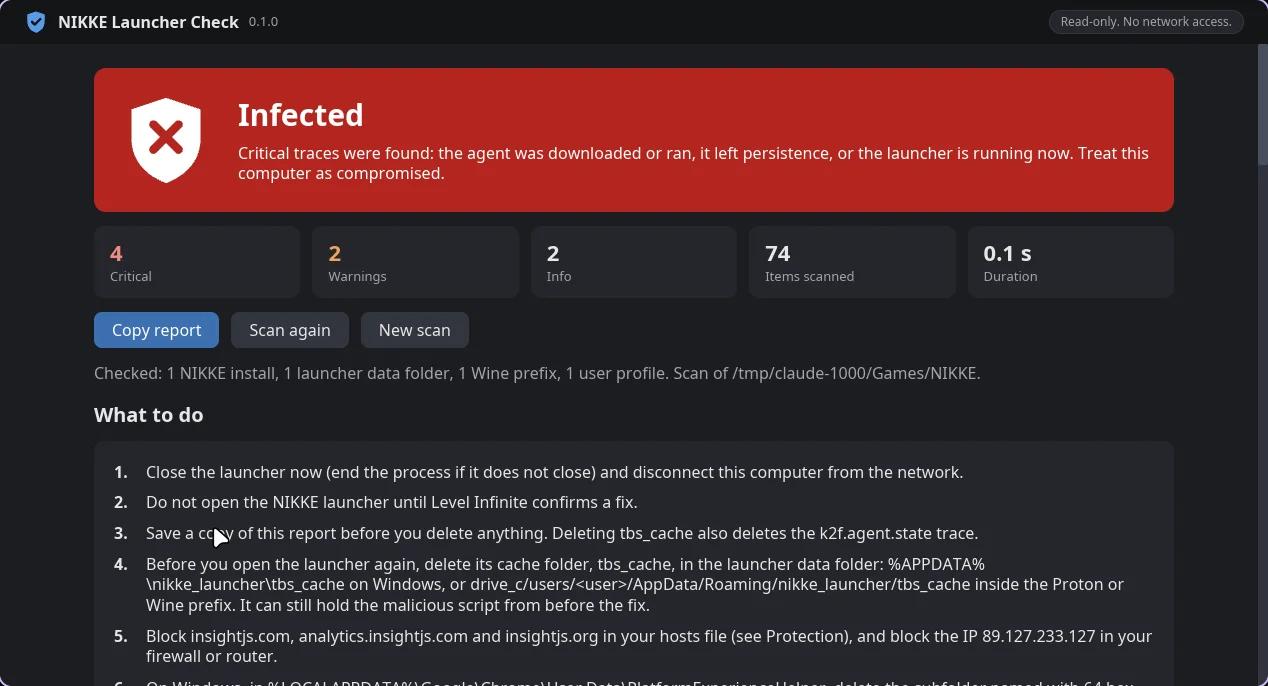
If k2f_chan registered is found in the log, it is decisive evidence that the agent actually executed. In this case, the PC's sensitive information should be considered exposed, and post-incident measures must be taken. However, not finding this trace in the log does not unconditionally mean the system is safe. The creator of the diagnostic tool 'nikke-check', distributed by MotherSphere, explicitly states that "finding nothing is not evidence that the computer is clean," and notes that the report itself is based on static analysis and limited infection cases 14.
AI API Keys and Account Cleanup Checklist
The sequence of measures recommended by the MotherSphere technical report is as follows.
Tampered files may remain in the Nikke PC launcher cache folder (%APPDATA%\nikke_launcher\tbs_cache), so this folder should be deleted before relaunching the launcher. It is also advisable to block attacker domains, such as insightjs.com, via the hosts file or router firewall 12. Since the hosts file cannot block IP addresses themselves, it should be used only for domain blocking 2.
- Core Account Changes: First, change the passwords for your Nikke and Level Infinite accounts. Then, sequentially change passwords for email, Discord, and banking sites.
- Two-Factor Authentication and Session Termination: Force log out of all devices and set up two-factor authentication again. If cookies remain, sessions may persist even after a password change 2.
- AI API Key Revocation: If you have saved API keys for OpenAI, Anthropic, OpenRouter, etc., while using AI coding or chatbots on this PC, revoke and reissue them immediately. API keys are easily included in text files, so if the agent can read those files, it is equivalent to an immediate leak 5.
- Developer and Cryptocurrency Wallet Measures: Replace SSH keys and cloud tokens. For cryptocurrencies, it is safer to create a new seed wallet and transfer funds.
MotherSphere's report recommends reinstalling Windows as the most certain method to completely remove malware if agent traces (k2f_chan) are found 512.
Ultimately, finding 'k2f_chan' in the log is the minimum baseline for determining whether your PC fell within the attacker's remote control scope. While it is confirmed that the agent was in a state where it could 'read' files on the PC, whether specific passwords or API keys were actually transmitted to the server is not recorded in the logs, necessitating individual checks 12. Therefore, if traces of agent execution are visible, revoking both AI API keys and passwords is the safest option at present, regardless of whether actual leakage occurred.
References
- NIKKE PC launcher compromise (Nov 2026): Level Infinite CDN files modified, remote-control agent, indicators · gist.github.com↩
- 니케 PC 런처 해킹, 임시 대처 방안 정리 · youtube.com↩
- BREAKING NEWS! SHIFT UP RESPONDS TO THE HACK! + UPDATE ON THE SITUATION! & WHAT'S GOING ON? (Nikke · youtube.com↩
- ↩
- 일반 이번 해킹사태 QnA 정리해옴 · arca.live↩